Home/Security & disclosure
DOZ security

Found a flaw? Tell us first

We protect your data and our fleet in layers, from app to lock. If you find a flaw, report it in good faith — we reply within 2 business days and will not pursue you legally.

Pre-launch preview — the policy takes effect at launch.

Protecting your data

Six plain commitments

A short summary — the full details are in the privacy policy. Privacy policy ←

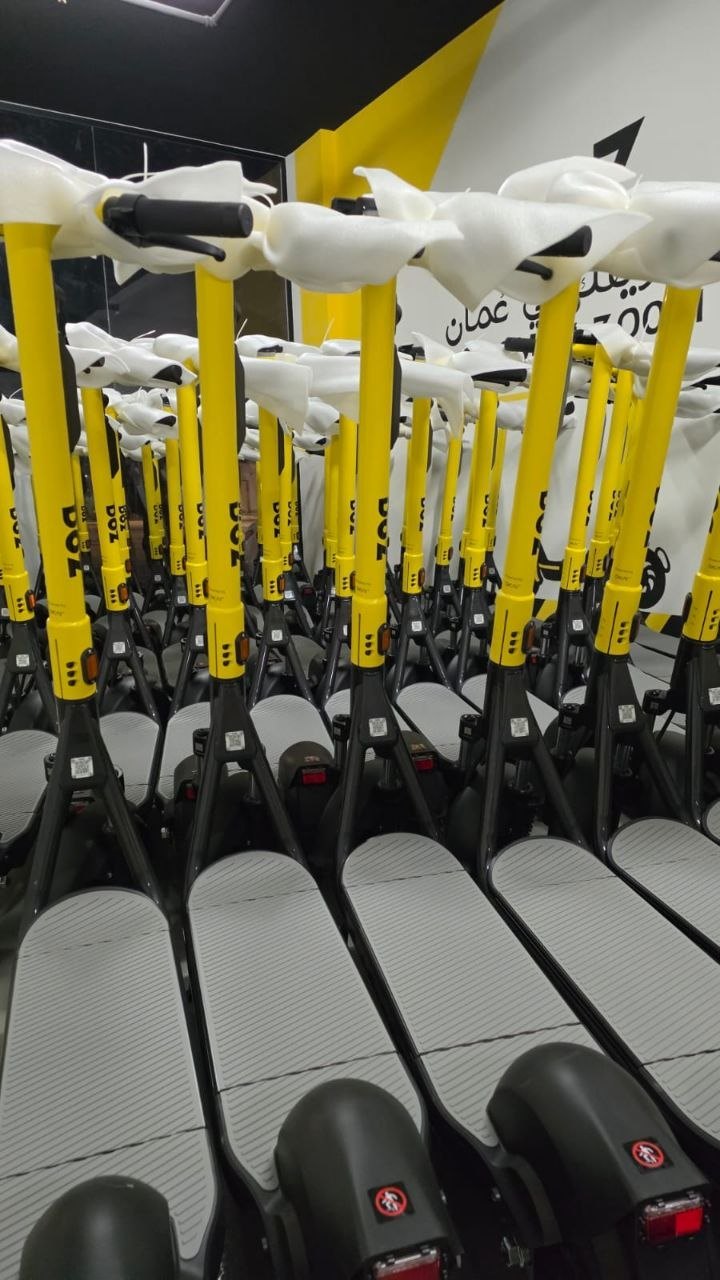
Rows of yellow DOZ scooters
Every scooter has a unique digital identity
Scooter & IoT security

Four layers between street and server

  1. 01
    Lock & IoT module

    A unique identity per scooter, secure boot and signed, encrypted firmware updates only.

  2. 02
    Connectivity

    Private SIM on an isolated network; unlock commands work only with a short-lived ride token.

  3. 03
    Scan & unlock

    A QR code alone is not enough — the server checks account, location and scooter state first.

  4. 04
    Monitoring

    Instant alert if a locked scooter moves or its cover opens, with remote lock on theft.

How to report

From your report to the fix

  1. 1Send your report

    To security@mob.doz.com: steps, impact and a link or screenshot — Arabic or English.

    Any time
  2. 2We confirm receipt

    A human reply with a tracking number, not just an auto-reply.

    Within 2 business days
  3. 3We verify and rate

    We reproduce it, rate it with CVSS and share the plan.

    Within 7 days
  4. 4We fix and credit you

    Critical first, then public thanks on the «Thanks board» if you wish.

    Critical ≤ 30 days

Fix targets by severity

  • CriticalUnlock without a ride, or rider data access≤ 30d
  • HighPayment bypass or account takeover≤ 45d
  • MediumLimited info leak or stored XSS≤ 60d
  • LowHeader config or issues with no direct impact≤ 90d
Scope

What you may test, and what not

In scope

  • DOZ rider app (Android & iOS)
  • Juicer app (charge & move)
  • Website and subdomains *.mob.doz.com
  • Partner API
  • Scooter unlock/lock and fleet commands

Out of scope

  • Denial-of-service or load flooding
  • Social engineering or phishing staff
  • Physically tampering with a scooter or its lock
  • Accessing other riders' accounts or data
  • Third-party services outside our control

Safe harbour

If you follow this policy — in good faith, without harming riders, disrupting the service or keeping their data — we will not take legal action against you and will treat your research as authorised.

Thanks board

The first name here could be yours

No reports yet — we are pre-launch. Every researcher who helps us is listed here by name or handle.

security@mob.doz.com

Researcher questions

Do you pay bounties?

Not before launch. We credit researchers publicly now; a paid bounty programme is planned after launch and will be announced here.

Can I test a scooter on the street?

No. Do not tamper with any scooter or test while someone rides. Ask us for a test unit and we will arrange it.

I saw another rider's data — what now?

Stop at once, do not keep or share it, and report with the minimum needed to prove the issue.

Can I publish my finding?

Yes, after the fix or 90 days after your report, whichever comes first — we agree the date with you.